Foreign spies, AUKUS and LinkedIn: Why Insider Threat Management is now a Frontline Business Control
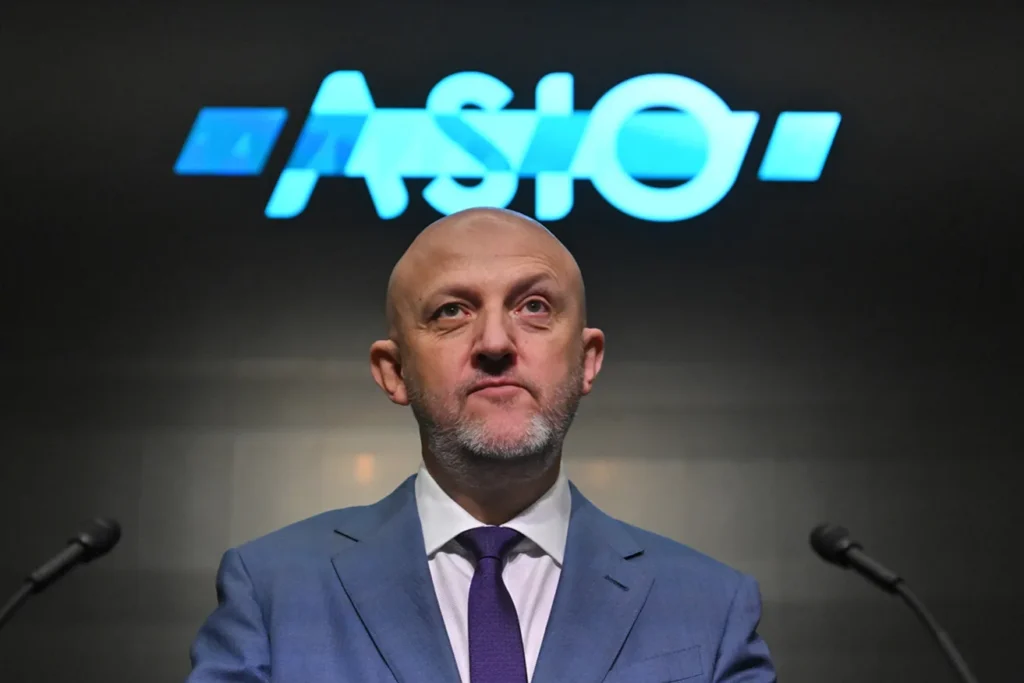
September 1, 2025 – When Australia’s domestic intelligence chief warns that foreign spies are actively targeting Defence employees working on AUKUS, it’s not an abstract, Cold War throwback—it’s a live operational risk for organisations across the supply chain. During his Hawke Lecture on 31 July 2025, ASIO Director-General, Mike Burgess, said public servants and private contractors are “making it easy for spies” by oversharing on professional platforms such as LinkedIn—advertising security clearances, project roles and access to sensitive programs. That online breadcrumb trail is now a recruitment pipeline for foreign intelligence services, and a liability for employers who are accountable for safeguarding people, information and assets.
In the same address, ASIO detailed a scale of activity that should focus every executive’s mind: 24 major espionage and foreign interference operations disrupted in three years, and an estimated $12.5 billion annual cost of espionage to the Australian economy. That impact spans intellectual property theft, compromised R&D, sensitive commercial data, and pre‑positioning for sabotage against critical infrastructure. This isn’t just a national security problem—it’s a business resilience problem that lands on boards, CEOs, CISOs and HR and security leaders alike.
Why “people security” is the control that changes everything
Most organisations have invested in perimeter technologies, policies and cyber controls. Yet investigations repeatedly show that insider risk—malicious or negligent—sits at the intersection of people, process and technology. That means decisive control isn’t a tool; it’s trained people making better decisions, supported by leadership, policy and practical pathways to report concerns early.
What is an insider?
An insider is any individual who has legitimate access to an organisation’s systems, facilities, or information—whether as an employee, contractor, consultant, or partner—and who uses that access, either intentionally or unintentionally, to cause harm. This harm can include data breaches, sabotage, espionage, fraud, or reputational damage. Importantly, insider threats are not always malicious; they often stem from negligence, stress, coercion, or lack of awareness. An effective program blends the Australian Government’s Protective Security Policy Framework (PSPF) with ASIO’s Countering the Insider Threat guidance and the Security of Critical Infrastructure (SOCI) Act obligations.
In plain terms:
– Know your risks (and map them to people‑asset touchpoints).
– Build culture and governance so staff understand obligations and feel safe to speak up.
– Detect and respond using both human observation and calibrated technical monitoring, such as DTEX Systems.
– Measure and improve—treat insider risk as a continuous capability, not a one‑off workshop.
Insider threat is a shared responsibility—by law
Insider Threat is no longer just the responsibility of Australia’s National Intelligence agencies. It must be a shared mission between government entities and the operators of our critical infrastructure. That’s why the SOCI Act was legislated in 2018—to embed insider-risk governance into the DNA of our national resilience strategy.
The SOCI Act applies to the following 11 critical infrastructure sectors:
– Communications
– Financial services and markets
– Data storage or processing
– Defence industry
– Higher education and research
– Energy
– Food and grocery
– Healthcare and medical
– Space technology
– Transport
– Water and sewerage
If we fail to take this responsibility seriously, the consequences are not abstract—they’re operational. A single insider incident could trigger cascading failures across energy, healthcare, transport, and communications. The result? A fractured economy, compromised public safety, and diminished sovereignty.
The SOCI Act mandates that critical infrastructure operators must assess and manage insider risks, implement training and awareness programs, and maintain incident response plans that include insider threat scenarios. This shared responsibility is not optional—it’s embedded in law. Treating insider risk as a compliance checkbox rather than a frontline control leaves organisations exposed to sabotage, espionage, and reputational damage.
What happens if we get this wrong? A scenario Australia can’t afford
Imagine this:
A Defence contractor working on a classified AUKUS project is targeted online after oversharing on LinkedIn. The individual, under financial stress and feeling undervalued, is recruited by a foreign intelligence service. Over several months, they exfiltrate sensitive project data using unauthorised USB devices and encrypted messaging apps—behaviours that went undetected due to weak insider-risk controls.
The stolen data includes schematics for a naval propulsion system and access credentials for a secure Defence communications node. Using this access, the adversary launches a coordinated cyberattack on Australia’s energy grid, targeting SCADA systems that control electricity distribution in major cities.
The result? A cascading blackout across eastern Australia:
Transport systems grind to a halt—airports, rail networks, and traffic control systems fail.
Communications collapse—mobile networks and internet services are disrupted, including emergency services.
Defence operations are paralysed—military bases lose power and secure comms, delaying mobilisation and compromising readiness.
Hospitals and critical care facilities switch to backup power, but fuel shortages loom within 48 hours.
Public trust erodes as misinformation spreads online, amplified by bot networks exploiting the chaos.
This isn’t science fiction. It’s a plausible, multi-domain threat scenario that reflects the interconnectedness of Australia’s critical infrastructure. As the CSIRO and Department of Home Affairs have warned, our systems are increasingly interdependent—and increasingly vulnerable to cascading failures.
The lesson? Insider threats are not just a personnel issue. They are a national resilience issue. And the cost of inaction is measured not just in dollars, but in lives, sovereignty, and strategic stability.
Australia’s insider‑threat capability is a strategic advantage—let’s match it with a whole‑of‑economy mission
Australia fields some of the best insider‑threat professionals across the Five Eyes community, working tirelessly behind the scenes to protect nationally sensitive information and critical infrastructure. It’s time for every entity—public and private—to match that professionalism with investment and discipline. Treat insider‑risk management as a whole‑of‑economy mission: resource it, measure it and rehearse it with the same seriousness you apply to financial controls, safety and disaster recovery.
Technology matters too
Training is the foundation, but technology amplifies its impact. Australian companies like DTEX Systems are leading globally in human‑centric insider‑risk platforms, helping organisations detect early behavioural indicators and protect data without compromising privacy. Pairing world‑class training with home‑grown technology gives Australia a decisive edge in countering insider threats.
From headline to checklist: immediate steps you can take this month
De‑risk professional profiles
Run a rapid review of employee LinkedIn entries for secuiry clearances, specific AUKUS/Defence project names, sensitive role descriptors, facility locations and similar breadcrumbs. Replace them with generic descriptors approved by your security team.
Baseline awareness for all staff
Deliver a short, evidence‑based insider‑threat awareness course to every employee and contractor—especially those with access to sensitive information or critical operational roles. Reinforce reporting channels and protections.
Role‑based people‑risk controls
Update role risk assessments, pre‑employment screening settings, and ongoing suitability checks proportionate to access and authority. Link this to SOCI and PSPF compliance artefacts and your annual security plan.
Trust‑and‑reporting culture
Signal from the top that asking for help early is the safest, most professional option. Establish confidential pathways and remove stigma around wellbeing or financial stress—many insider‑risk pathways begin as human problems, not malicious intent.
Practice the response
Run a tabletop on a realistic scenario: online targeting of an engineer who has overshared on social media, followed by anomalous data access and off‑network transfers. Exercise HR‑Legal‑Security coordination and the threshold for external reporting.
What “good” insider‑threat training looks like
The outcome we must aim for is clear: a workforce that knows what not to post, understands how they are targeted, spots anomalies early, and reports concerns safely—and a leadership group that treats insider-risk governance as a frontline control, not a compliance checkbox.
The public warnings are unambiguous: foreign services have a “very unhealthy interest” in AUKUS and the Australian Defence ecosystem. Turning that headline into action means treating insider‑threat training as a core control—as routine as patching, backups, and financial delegations. The dividend is resilience: fewer near‑misses, earlier interventions, and fewer headlines.
Karen Bradley, Director, MPS People Security Risk Management, Canberra
MPS People Security Risk Management Pty Ltd (MPS People Security) specialises in Insider Threat programs and training and has been a leading force in the Australian security industry since the inception of its parent company, Mitchell Personnel Solutions (MPS), in 2006. The company has consistently delivered security services aligned with evolving political and legislative priorities, supporting the Australian Government for over 20 years.